The short answer
For most workstations, the right model is a standard user, temporary controlled elevation for approved tasks and Windows LAPS for recovery access. A permanent local administrator account should remain only a documented exception. LAPS protects a unique local password; Endpoint Privilege Management elevates a specific task. The functions complement each other and must be tested with real applications.
- Standard user by default
- EPM for a known, approved task
- LAPS for local recovery
- Separate account for full administration
- Permanent exception with owner and deadline
Distinguish the account, password and elevated task
The debate becomes simple when three objects are separated. A permanent administrator account gives a person or process lasting power over a workstation. Windows LAPS manages and renews a local account's secret; it does not decide which applications an employee can elevate. Endpoint Privilege Management (EPM) allows a specific task to run with higher privileges without placing the user in the Administrators group.
This avoids two common mistakes: using the LAPS password for everyday installation, or believing EPM replaces every local recovery path. The first spreads a powerful secret and weakens traceability. The second leaves the team without a solution when the device no longer communicates correctly with the cloud. Robust architecture provides a normal path, an exception path and a recovery path.
Why do permanent privileges increase risk?
An administrator user can install drivers, modify services, disable protections and write to sensitive locations. The same power becomes available to malware running in that session. An error or phishing attempt is therefore no longer limited to the user profile: it can affect the whole system, other local accounts and security mechanisms.
The issue is not just administrator numbers. You need to know privilege duration, the identity using it, authorised actions and rapid revocation options. A separate account is preferable to everyday work with a powerful account, but remains lasting privilege. Least privilege reduces both scope and exposure time.
Which models should you compare?
Four models occur in practice. The first keeps the daily account in local administrators: simple but hard to control. The second creates a separate named administrative account: better separation, but still permanent power. The third uses Windows LAPS for a local recovery account with a unique, renewed password. The fourth keeps the user standard and elevates an approved application with EPM.
The best outcome is usually a combination. Known recurring tasks use an elevation rule. Full interventions remain for authorised technicians. LAPS protects recovery of an isolated workstation. Persistent exceptions have an end date, owner and justification.
What Windows LAPS does and does not do
Windows LAPS automates management and backup of a local administrator password. Each device can receive a different secret, renewed according to policy and recoverable by authorised roles. Microsoft documentation updated on 16 September 2026 explains that backup can target Microsoft Entra ID or Active Directory depending on join type. A hybrid device chooses one destination; it does not back up to both simultaneously.
LAPS reduces the risk of the same local password being shared across a fleet and simplifies rotation after use. It does not automatically make an application an approved task, replace identity management or justify sharing the password with the user. Treat reading it as sensitive: minimal role, logging, procedure and rotation after use.
Microsoft states that Windows LAPS is available at no additional cost on supported Windows platforms, while some associated Intune or Entra features require their own licence. Always check edition, version and tenant licensing before deployment.
What just-in-time elevation offers
EPM lets a standard user elevate an executable, MSI installer or PowerShell script according to a rule. The rule can recognise publisher, certificate, hash, name or path, and control arguments and child process behaviour. Microsoft documents automatic elevation, user confirmation, support-approved requests or denial.
Elevation targets the task, not the whole session. It suits a business utility, controlled update or recurring diagnostic action. An overly broad rule nevertheless recreates permanent privilege in another form. Allowing any file in a writable folder or every binary signed by a broad publisher may create a bypass.
EPM requires an eligible licence; terms must be checked in the current tenant and contract. This article includes no price because cost depends on the plan and may change.
How do you choose according to need?
The decision starts with need, frequency and control level. A rare full intervention calls for a different solution from a known application needing elevated rights weekly. The table compares scope, duration, traceability, offline operation and recommended use.
| Model | Scope and duration | Traceability | Limitation | Best choice according to need |
|---|---|---|---|---|
| Daily administrator account | Whole workstation, lasting | Immediate | Weak separation; high risk | Very temporary exception |
| Separate admin account | Whole workstation, lasting | Good if named | Still permanent power | Full administration by technician |
| Windows LAPS | Local recovery account | Traceable reading and rotation | Not task elevation | Emergency access, offline, recovery |
| EPM / JIT | Approved file or task | Rules and reports | Licence and rule design | Targeted recurring tasks |
Inventory actual elevation requests
Collect requests over a representative period before removing rights. Classify by application, publisher, version, site, role, frequency and expected result. Distinguish one-off installation from a daily function unnecessarily requiring administration. Some applications can run as standard after fixing a folder, registry key or update mechanism.
Ask support, field teams and application owners. Cases invisible at headquarters often appear in a laboratory, workshop, classroom or practice: old peripherals, card readers, nomenclature updates, tax plugins, print drivers or diagnostic tools. Record offline situations and acceptable delays too. The resulting catalogue becomes the basis for rules and the pilot.
GVISION can incorporate this work into endpoint management with Microsoft Intune, with groups, rings and deployment evidence tailored to the populations involved.
Design rules that are hard to bypass
A good rule is narrow, readable and reviewable. Prefer a trusted publisher or certificate, supplemented by product and version where sufficient. A hash is very precise but must be updated for every new version. A path alone is fragile if the user can place or replace a file there. Check arguments, child processes, called files and update mechanisms.
Choose the least permissive response compatible with business needs. Automatic elevation suits a tightly controlled task. Confirmation with justification adds a signal. Support approval is useful for a rare or riskier request, provided the delay is acceptable. Explicit denial protects against an unexpected broad rule.
For every rule, document its owner, reason, groups, test evidence, review date and removal procedure. A rule without an owner quickly becomes security debt.
Connect local privileges and identity
Endpoint security also depends on the identity retrieving the LAPS secret or approving elevation. Limit these roles, require strong authentication, separate administrative accounts and monitor usage. A technician should not automatically have all secrets across the estate if their scope is limited to one site or team.
The Microsoft Entra identity governance helps structure groups, roles and access conditions. The aim is to link each privileged action to a named identity, device and context. For shared accounts or out-of-band procedures, keep a usage register and trigger rotation as soon as the secret has been used.
GVISION also recommends testing role removal: can an organisation actually revoke a technician, supplier or compromised account without blocking continuity?
Plan for failures, offline use and recovery
An endpoint may be off-network, poorly synchronised or unable to apply a new policy. The plan must specify which EPM rules remain available, how support requests are handled and under what conditions the LAPS-managed account is used. Do not promise immediate cloud approval at a site without reliable connectivity.
The recovery procedure states who may read the password, how to verify the requester’s identity, where to log the ticket, which actions are allowed and when to force rotation. Avoid sending the secret through an uncontrolled channel. When the device comes back online, check logs, compliance status and changes made.
Also test the negative scenario: password unavailable, account disabled, rotation incomplete or technician without access. An untested fallback remains an assumption.
Deploy in rings and measure
Start with a representative lab, then IT support, a small business group, a pilot site and finally larger rollout waves. Each ring should include easy and difficult applications, fixed and mobile endpoints and at least one offline case. Define rollback criteria before removing rights.
Measure successful task rates, blocked requests, processing time, rules created, exceptions and security incidents. Fewer tickets are not enough if users bypass the system. Conversely, a temporary rise in requests may simply reveal previously invisible needs.
The package photograph illustrates joint testing by support and the business team. The user confirms that work is possible; IT confirms that elevation remains limited and observable.
Adapt the service desk process
Support must recognise four situations: an already approved application, a known request requiring approval, a need for full administration and suspicious behaviour. Provide a short form with device, application, action, business urgency and an error screenshot. The analyst must not request the personal password or reflexively add the user to the Administrators group.
For approval, check the file source, signature, hash where relevant and business owner. In an emergency, use a separate administrative account or the LAPS procedure, then document and rotate the secret. A closed ticket includes the result, privilege duration and any rule needing review.
Prepare simple messages. Explain that removing rights is not intended to slow work down: it replaces permanent power with a controlled, supported action.
Belgian examples by sector
In a school, EPM can authorise an educational tool or controlled driver, while LAPS serves the technician at an isolated endpoint. In a healthcare facility, changes to a terminal linked to a device require application and clinical approval; elevation never replaces that governance. In a professional practice, a signed tax update can be approved without giving every staff member permanent power.
A multi-site group must delegate without opening the entire estate: regional groups, a common procedure and limited LAPS access. A public administration must retain approval evidence and separation of duties. A non-profit with limited support should favour simple rules, a small catalogue and a clearly documented assistance route.
Size does not determine the level of control. Risk, frequency, business dependency and support capacity guide the model.
Common mistakes to avoid
Do not remove all rights on a Friday without an inventory or pilot. Do not create a rule elevating everything in Downloads. Do not give the LAPS password to the user for convenience. Do not leave support approval without a target response time, or teams will find workarounds.
Also avoid shared administrator accounts, no rotation after use, exceptions without expiry and rules based solely on a filename. Do not assume a publisher signature is sufficient for all its products. Finally, do not confuse logging with prevention: a report supports investigation, but an overly broad rule remains dangerous.
The final review must cover user experience, offline operation, recovery, revocation and evidence quality.
Eight-step implementation plan
Start by defining policy: standard user by default, named exceptions and recovery criteria. Then inventory accounts, local groups, applications and elevated tasks. Enable LAPS on a pilot group, configure read roles and verify rotation. Deploy EPM in observation mode and create a few precise rules for the most frequent needs.
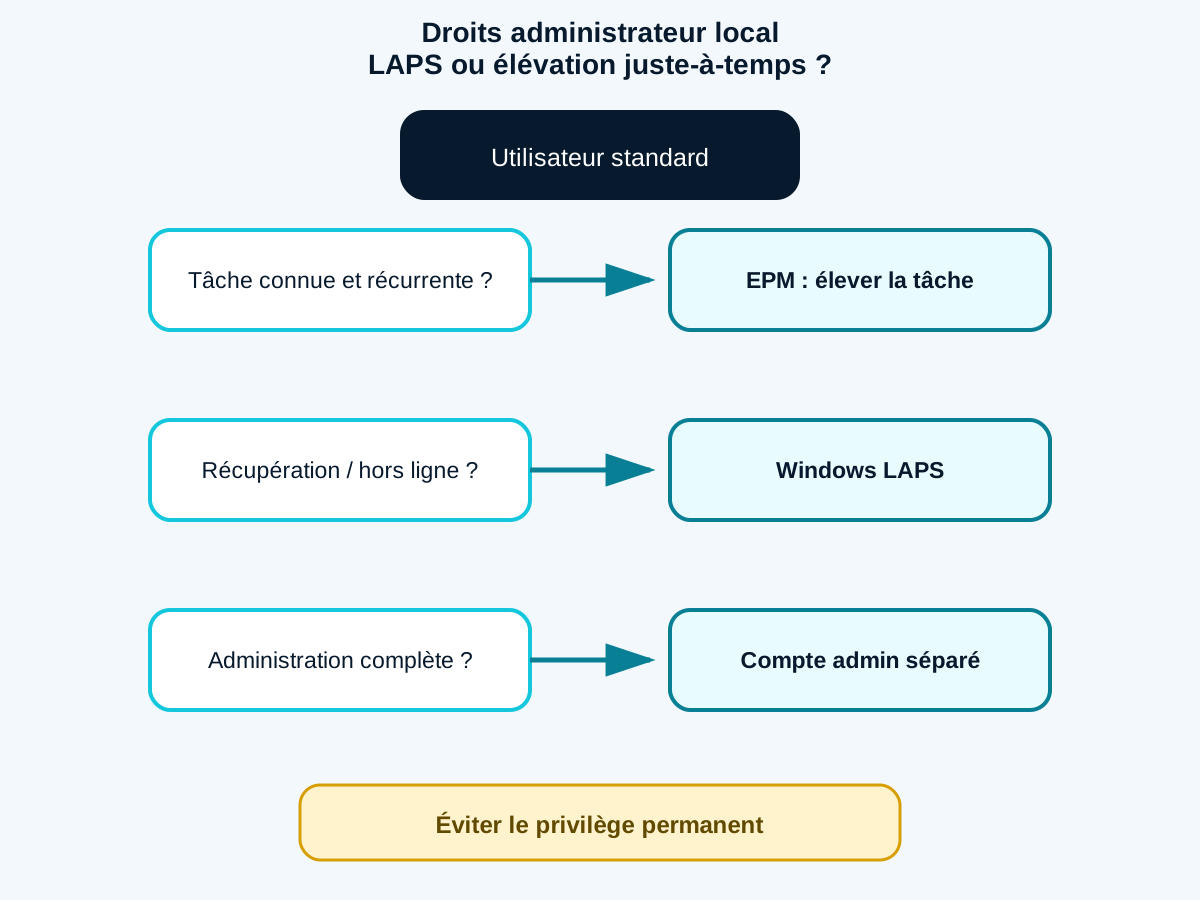
Test with business teams, train the service desk, gradually remove local memberships and monitor requests. Finally, review rules and exceptions at a fixed frequency. For every stage, retain the decision, result and owner. The visual matrix summarises the approach: EPM for a known task, LAPS for recovery, a separate account for full administration and a permanent account only as a temporary exception.
A successful deployment is measured not by the number of rights removed in a day, but by the sustained ability to work and troubleshoot without unnecessary privilege.
Frequently asked questions
Does Windows LAPS replace EPM?
No. LAPS manages the password of a local recovery account. EPM elevates a specific task for a standard user.
Should all local administrator accounts be removed?
Not necessarily. Keep a controlled recovery route, but remove unnecessary permanent memberships.
Does EPM work for all file types?
Microsoft documents elevation for EXE, MSI and PowerShell scripts. Applications and dependencies must be tested.
Can the LAPS password be given to the user?
This is not a recommended daily model. Retrieval must remain controlled, logged and followed by rotation.
Which rule is safer: publisher or hash?
A hash is precise but fragile across updates. Publisher rules are more durable but must be limited. Context determines the combination.
How do you manage an offline endpoint?
Provide offline-available rules and a LAPS recovery procedure with verification, a ticket and rotation.
How long does a pilot last?
Long enough to cover real application cycles, sites, mobile users and at least one failure scenario.
Conclusion: remove privilege, retain the ability to act
The target model combines standard users, per-task elevation and protected recovery. Start with real uses, test exceptions and measure support. GVISION can help you scope a pilot with GVISION.
Official sources
Published on . Updated on .
Let’s talk about your project
Want to apply this advice in your organisation? Let's review your needs and next steps together.
Talk to GVISION