The short answer
To secure guest Wi-Fi, create a separate SSID linked to a dedicated VLAN, block all internal network access by default, enable client isolation and allow only necessary services to the internet. Then add bandwidth limits, an access duration, proportionate logging and tests from a real visitor device. A captive portal improves the welcome experience but never replaces segmentation.
- A different network name is not security separation.
- The guest VLAN must be controlled by explicit firewall rules.
- Client isolation prevents two visitors from communicating directly.
- The captive portal handles the welcome and terms of use, not LAN protection.
- Validation must cover IPv4, IPv6, DNS, internal devices and multiple sites.
What is the real objective of guest Wi-Fi?
The aim is not just to provide internet: an unknown device must be contained in an area where an error, infection or probing attempt cannot reach internal operations. A visitor may arrive with a perfectly clean phone, a misconfigured business computer or an already compromised device. The organisation controls neither updates, applications nor the user. Trust must therefore be minimal by default.
On NIST SP 800-153 guide notes that WLAN security depends on design, configuration and monitoring throughout its lifecycle, not just radio encryption. This is a useful distinction: WPA2 or WPA3 protects the wireless link, while segmentation determines what a device can reach once connected. These protections address different problems.
Before configuring a Wi-Fi controller, express the policy in one testable sentence: “a guest can resolve names, obtain the time and access the internet, but cannot reach any private network, other guest or equipment administration”. This sentence then becomes a list of rules and tests. To scope coverage, capacity and equipment, the page on GVISION professional networks and Wi-Fi presents the main service associated with this architecture.
Recommended architecture: SSID, VLAN, firewall and isolation
A robust architecture has four successive barriers: a visitor-only SSID, its own VLAN and subnet, a firewall between that network and the rest of the organisation, then client isolation on Wi-Fi. No barrier should be considered sufficient on its own.
The SSID identifies usage
The network name helps users choose the right connection and allows a policy to be associated in the controller. It does not automatically create a boundary. Two SSIDs can still lead to the same VLAN if mapping is wrong. A visual controller audit is therefore insufficient: check the assigned IP address, gateway and actual path taken.
The VLAN separates network domains
The guest VLAN must have its own addressing plan and must not be used by workstations, printers, cameras, phones or industrial equipment. In a multi-switch network, the VLAN must traverse only necessary trunks. A forgotten access port or poorly chosen “native VLAN” can create an unexpected shortcut. Document the identifier, subnet, DHCP, gateway and sites involved.
The firewall decides, local isolation complements it
Inter-VLAN routing must pass through equipment enforcing a policy. The fundamental rule is an explicit deny towards internal ranges, followed by limited permissions for required services. Client isolation, sometimes called client isolation or peer-to-peer blocking, also prevents two guest devices associated with the same access point from reaching each other directly. Depending on manufacturer and architecture, this option must be validated between two access points, not just on one.

Compare four ways to provide guest access
The best choice depends on risk, visitor numbers and network maturity, but sharing the staff LAN is not an acceptable guest model. A small site can work with a VLAN and simple rules; a campus or multi-site environment may need temporary identities, NAC or dynamic policies.
| Model | Separation | Benefits | Limitations | Use case |
|---|---|---|---|---|
| Password on the internal LAN | No real separation | Immediate setup | Exposes internal resources and complicates revocation | Avoid |
| Guest SSID with local isolation | Clients separated, depends on network mapping | Simple for a very small site | Insufficient if the SSID still joins the LAN | Transitional step only |
| SSID + VLAN + firewall | Controlled network boundary | Clear, testable, suitable for many sites | Requires consistent end-to-end configuration | Default choice for most organisations |
| Guest access with identity/NAC | Policy per user, device or sponsor | Traceability and customised durations | More complex cost and operations | Campuses, multi-site groups, recurring visitors |
| Best choice according to need | VLAN and firewall for clear isolation; identity/NAC when profiles, sponsors and durations need granular management. | |||
Which firewall rules should you apply?
Start with a default deny towards internal networks, then allow only flows required for the guest service to work. Rule order matters. A broad “LAN to any” rule placed before the block can undermine the entire architecture. Give objects and rules understandable names, with an owner and a rationale.
The guest network generally needs DHCP to receive configuration, DNS to resolve names and NTP for time. Depending on architecture, these services may be provided by the firewall, a dedicated resolver or external services. If internal DNS is used, avoid unnecessarily revealing internal names and prohibit queries to other DNS servers when policy requires it. Outbound web access can be filtered according to organisational rules.
Block all private ranges used by the company, management interfaces, Wi-Fi controllers, switches, hypervisors, NAS, printers, cameras, IP phones and technical equipment. Do not settle for one RFC 1918 range when multiple private networks, VPN links or cloud routes exist. Also check IPv6: perfect IPv4 filtering does not prevent an overlooked IPv6 route.
A policy can also limit outbound ports, bandwidth per client, total volume, session duration or device numbers. These are availability and quality measures, not substitutes for isolation. For rules, management VPNs and boundaries between zones, the page on firewalls, VPN and ZTNA explores the complementary control layer.
Is a captive portal mandatory?
No: a captive portal is a decision about welcome, identification and terms of use; fundamental security still comes from segmentation. An organisation can offer a regularly changed password, temporary codes, sponsored access or a portal. The choice depends on visitor frequency, acceptable support levels and the need to link a session to a person.
A portal can display usage rules, a validity period and a support contact. Avoid requesting an email address, phone number or full identity 'because the option exists'. Once personal data is collected or retained, GDPR principles apply, including purpose limitation, minimisation, retention periods, transparency and security. GDPR Article 5 is the primary reference; specific legal needs should be validated with the organisation's DPO or legal adviser.
Captive portals can also cause practical difficulties: a window failing to open, an incorrectly presented certificate, blocked redirection, an already active VPN, a browserless device or a missing translation. Provide a clear fallback. A QR code can simplify connection, but must point to the correct SSID and be replaced when the secret changes. Never display a password giving access to the internal network.
How do you prevent guests from saturating the network?
Size radio and internet capacity for real peaks, then apply fair limits rather than an arbitrarily low speed that makes the service unusable. One hundred connected phones during a meeting do not consume resources like ten consultants on video calls. Observe device numbers, radio contention, signal quality and WAN bandwidth separately.
Reserve part of the connection for business applications and VoIP through quality of service. Consider limiting bandwidth per device and categories clearly incompatible with intended use. A school open day, hotel, waiting room and consulting office have different profiles. Measure peak hours before changing radio settings or adding access points.
Deploy guest Wi-Fi in ten steps
Successful deployment starts with a policy and ends with test evidence, not simply creating the SSID. Use a controlled window and retain rollback if the existing infrastructure already carries voice, cameras or other sensitive services.
- Inventory: access points, controller, switches, trunks, firewall, DHCP, DNS, cloud routes and VPN.
- Define uses: occasional visitors, recurring providers, events, browserless devices and meeting needs.
- Write the policy: allowed and prohibited destinations, duration, bandwidth and operational responsibility.
- Reserve the network: VLAN, subnet, DHCP range, gateway and naming conventions.
- Configure transport: SSID-to-VLAN mapping, strictly necessary trunks and no guest VLAN on unnecessary ports.
- Create rules: deny internal access, minimal technical permissions, filtered internet and IPv6 handling.
- Configure access: WPA2/WPA3 according to compatibility, client isolation, secret or portal and session duration.
- Protect capacity: per-client limits, business priorities, bandwidth monitoring and alert thresholds.
- Test: multiple devices and access points, DHCP renewal, roaming, DNS, user VPN and attempts to access the LAN.
- Document: diagram, rules, welcome procedure, owner, review date and validation evidence.
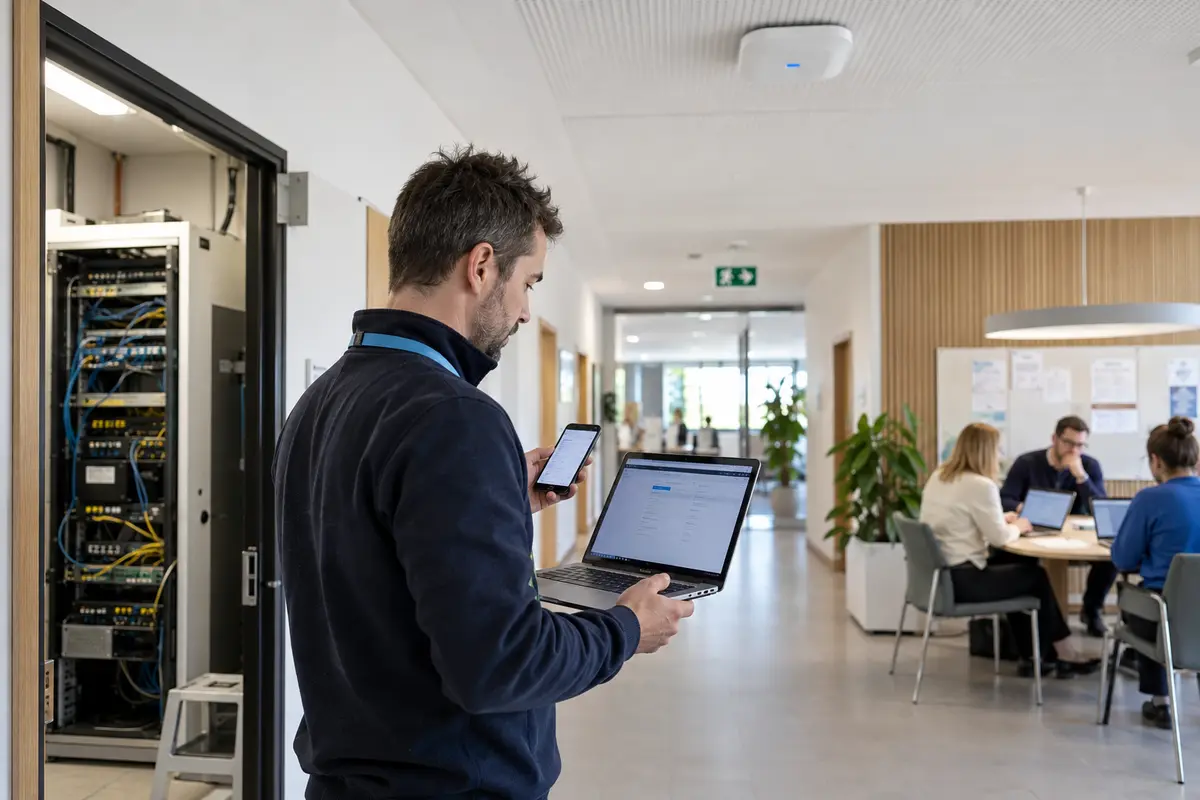
The validation checklist before opening access
A test is conclusive only when it proves both what works and what remains inaccessible. A web page opening confirms internet access, but does not prove servers are isolated. Document the device, access point, address received, time and expected result.
- Connect and disconnect with a new device, then a known device.
- Obtain an address belonging exclusively to the guest subnet.
- DNS resolution and HTTPS access to several legitimate internet services.
- Block internal gateways, servers, NAS, printers, cameras and network interfaces.
- Block access between two guest clients, including on different access points.
- Check IPv6, VPN routes and private networks accessible through the cloud.
- Portal operation on iOS, Android, Windows and macOS if these devices are expected.
- Code or session expiry, DHCP renewal and early revocation.
- Bandwidth limit, maintained VoIP and no degradation of priority applications.
- Useful events present in logs without excessive collection.
Finally, run a negative test from a secondary site. Centralised configurations can hide differences in trunks, firmware or local rules. In a multi-site group, a 'site × SSID × VLAN × gateway × policy' matrix is more reliable than assuming all sites are identical.
Practical examples for Belgian organisations
The technical foundation remains the same, but journeys and exceptions need to follow each organisation's reality. In a school, guest access can open for parent meetings and events without joining teaching, administrative or display networks. Regular visitors can receive longer-validity codes, while managed staff devices use separate authentication.
In a healthcare facility or practice, visitors must remain separate from records, devices, printers and staff workstations. The portal should not request health data. The waiting room needs a stable connection, but clinical traffic retains priority. Technical providers should not use guest Wi-Fi to administer equipment: separate, limited and logged maintenance access is more appropriate.
Common mistakes to avoid
Incidents rarely stem from the SSID name; they arise from an overly broad rule, inconsistent mapping or an untested change. The first mistake is creating 'Guest' in the controller without checking the VLAN actually assigned. The second is blocking only one internal subnet while routes to other sites, Azure, a data centre or a VPN remain accessible.
The third is treating the portal as a firewall. Accepting terms does not restrict any packet. The fourth is forgetting IPv6 or client isolation. The fifth is reusing a secret for years, shared in photos and emails. The sixth is imposing burdensome authentication on every visitor without a defined need, increasing support without improving the network boundary.
Maintain guest Wi-Fi over time
A guest network stays secure when rules, firmware, certificates, secrets and test evidence are reviewed on a defined cycle. Monitor client peaks, DHCP failures, radio saturation, unusual volume and configuration changes. Alerts should lead to a clear action, not just fill an inbox.
Review access when a site opens, moves or receives a new service: IP telephony, displays, cameras, printers, a Teams room, payment terminal or connected device. Each new VLAN or VPN may create a destination the old blocking rule misses. A rule using a centrally maintained 'internal networks' object group is often more robust than manually copied addresses.
FAQ on business guest Wi-Fi
Is a separate SSID enough to isolate guests?
No. The SSID needs a separate VLAN and firewall policy. Check the address received and test internal destinations, as two SSIDs may accidentally map to the same network.
Should you use WPA2 or WPA3 for visitors?
Use the strongest level compatible with expected devices and organisational policy. WPA3 brings improvements, but older devices may require a transition. Encryption never replaces network isolation.
Does a captive portal make the network more secure?
It can manage terms, codes and duration, but does not block LAN access. Separation relies on the VLAN, firewall and client isolation.
Can guests use a VPN?
Often yes, if required protocols are allowed. Test common visitor VPNs without unnecessarily opening internal traffic. An overly restrictive policy can prevent consultants from working.
Should every visitor's identity be collected?
Only when a real, documented purpose justifies it. Minimise data, inform people and define retention. Ask the DPO for advice on sensitive cases.
How do you share a printer or meeting display?
Publish only the necessary service through a controlled gateway or place the equipment in a dedicated zone with targeted rules. Do not open the entire internal network to meet a projection need.
How often should guest Wi-Fi be tested?
After every network, firewall, controller, firmware, VPN or site change, then periodically according to risk. Annual testing may be insufficient for infrastructure changing every month.
Simple access for visitors, a clear boundary for the organisation
Good guest Wi-Fi is barely noticed: connection works, internet applications respond and the user needs no manual. Quality is measured mainly by what remains inaccessible, capacity preserved for business and how easily IT can explain and verify the policy.
GVISION can map the existing environment, design segmentation, configure equipment and validate results across your sites. To scope a deployment or correct existing guest access, you can talk to the GVISION team in Belgium.
Official sources
Published on . Updated on .
Let’s talk about your project
Want to apply this advice in your organisation? Let's review your needs and next steps together.
Talk to GVISION