Microsoft 365 · 2026-09-17
A decision guide for collaborating with customers, suppliers, administrators and partners without turning every sharing action into permanent access.
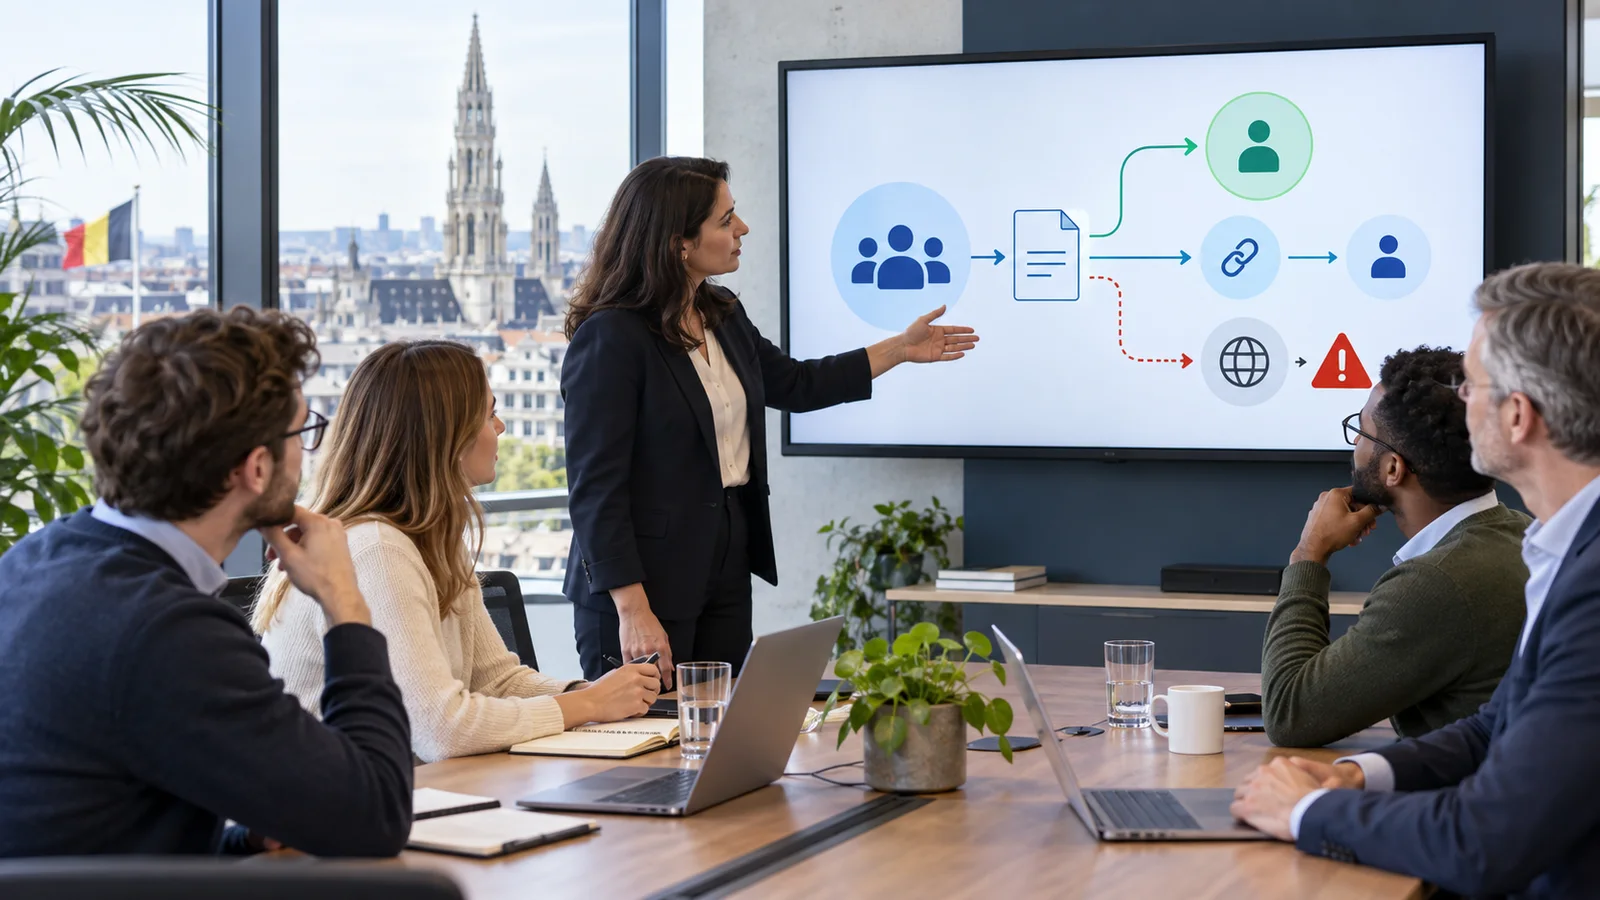
Which mode should you choose in one minute?
Use an authenticated guest when an external person participates in a project, accesses several libraries, joins a team or needs to retain long-term access. Use “Specific people” for a folder or document shared with known recipients without opening the entire site. An “Anyone” link is suitable only if the content may circulate beyond the original recipients and the absence of authentication is acceptable.
Ask five questions before sharing: who needs access, to what, for how long, with what permission and how will access be removed? If one answer is missing, do not choose the quickest option by default. The convenience felt at the time of sharing can create forgotten access, an absent owner or a link that cannot be attributed to an individual several months later.
The’Microsoft SharePoint support from GVISION covers the structuring of sites, libraries, permissions and usage. The article focuses on the external-sharing decision: it complements the service page without replacing tenant-level planning.
Which SharePoint mechanisms should you distinguish?
SharePoint combines a tenant-level sharing setting, a site-level setting, site permissions and links applied to a file or folder. These layers combine. An option visible in the dialogue does not mean it is suitable for the content; an absent option may result from a more restrictive rule defined at a higher level.
Microsoft describes four levels of external sharing for a site: organisation-only, existing guests, new and existing guests, and anyone. The tenant setting determines the maximum permitted level. A site can be more restrictive, but cannot exceed this ceiling. This relationship is explained in theofficial overview of external sharing in SharePoint and OneDrive, updated on 7 May 2026.
Link types answer a different question. “People in your organisation” remains internal. “People with existing access” does not grant a new permission: it provides a link to content that is already authorised. “Specific people” ties access to designated addresses. “Anyone” allows anyone with the link to access the content, subject to tenant and site settings.
How do you compare guest access, specific links and anonymous links?
Compare identity control, scope, duration, collaboration and removal. A guest is not inherently secure: they may receive excessive permissions and remain active for too long. A specific link is not automatically temporary. An anonymous link is not always prohibited, but it requires the content to tolerate circulation without attribution.
The table indicates the choice according to the need. Check expiry and reviews.
| Criterion | B2B guest / group | Specific people | Anyone |
|---|---|---|---|
| Identity | Authenticated guest object | Designated addresses | No authentication |
| Scope | Site, group, library or resources | Targeted file or folder | Targeted file or folder |
| Collaboration | Long-term and structured | One-off or limited | Distribution without identity |
| Advantage | Central management and policies | Forwarding is not enough to open | Very simple access |
| Limitation | Lifecycle to administer | May remain active for too long | Transferable link and limited attribution |
| Use cases | Project, partner, consultancy | Collection or delivery to known recipients | Public or non-sensitive content |
| Best choice according to the need | Ongoing relationship | Named individuals | Intentionally open circulation |
B2B guest / group
- Identity
- Authenticated guest object
- Scope
- Site, group, library or resources
- Collaboration
- Long-term and structured
- Advantage
- Central management and policies
- Limitation
- Lifecycle to administer
- Use cases
- Project, partner, consultancy
- Best choice according to the need
- Ongoing relationship
Specific people
- Identity
- Designated addresses
- Scope
- Targeted file or folder
- Collaboration
- One-off or limited
- Advantage
- Forwarding is not enough to open
- Limitation
- May remain active for too long
- Use cases
- Collection or delivery to known recipients
- Best choice according to the need
- Named individuals
Anyone
- Identity
- No authentication
- Scope
- Targeted file or folder
- Collaboration
- Distribution without identity
- Advantage
- Very simple access
- Limitation
- Transferable link and limited attribution
- Use cases
- Public or non-sensitive content
- Best choice according to the need
- Intentionally open circulation
Why is scope more important than the button?
Access to a site, library, folder and file does not have the same reach. For continuous collaboration, a dedicated site or library is often clearer than accumulating exceptions on folders. For one-off exchanges, a link to a file may be sufficient. Avoid sharing the entire site simply because several documents are spread across it.
Breaking permission inheritance can solve an isolated case, but makes governance more difficult when exceptions multiply. Map the spaces that host external users and separate them from sensitive internal content. A project site with identified owners, simple groups and an end date will generally be easier to review than a large intranet containing dozens of unique shares.
The business owner decides who still needs access; IT sets the guardrails and provides visibility.
When should you use “Specific people”?
This link is suitable when a file or folder must be accessible to a known list. Even if the message is forwarded, only the people authorised for the link should be able to use it. The recipient must prove their identity through their account or the method offered by the tenant. This reduces the risk of simple forwarding, without replacing verification of the correct recipient and content.
Use it to deliver documents to a customer, provide access to a few suppliers or share a short-term working folder that does not require membership of a site. Grant read access by default; allow editing only when the process requires it. Do not silently use a specific link as a substitute for a project space that will last a year.
Set a review date. If the recipient changes address or leaves their organisation, reassess access.
When should you create a Microsoft Entra B2B guest?
A guest is suitable for a lasting and identifiable relationship: consultant, board adviser, project supplier, partner or service provider joining a group, site or several resources. Microsoft Entra B2B creates an external user object in the tenant and allows the partner to use their own identity. This object can be added to groups, subjected to policies and centrally removed.
Documentation Microsoft Entra B2B, updated on 25 April 2026, states that the host organisation retains control of its data while the partner uses their own credentials. It distinguishes external collaboration settings, which govern invitations, from cross-tenant settings, which control authentication between organisations.
The GVISION page dedicated to identity management with Microsoft Entra provides identity and access context. In SharePoint, add the guest to a role-based group rather than assigning permissions arbitrarily. Designate a sponsor or owner, an end date and a procedure for when the relationship changes.
When is an “Anyone” link acceptable?
An “Anyone” link does not require authentication. Anyone who obtains it can use it while it remains valid and the policy permits it. It is therefore unsuitable for sensitive personal data, confidential contracts, security plans or information for which every reader must be identified.
It can be useful for a public brochure, a large file intended for broad distribution, an already-public document or a temporary repository whose leakage would not cause significant harm. Limit it to read-only access where possible, impose an expiry date if the feature is available and avoid download or editing when these restrictions meet the requirement. The exact availability of options varies by configuration.
The reasoning should be documented: non-sensitive content, expected distribution, short duration, owner and replacement channel. If you need to know who viewed the document, an anonymous link is the wrong mechanism. Prefer identified recipients.
How does the external user authenticate?
A partner with a Microsoft Entra business account will generally use their existing identity. A recipient without a compatible method may use a one-time passcode sent by email when this feature is enabled. Microsoft states that email one-time passcode is enabled by default for new tenants and tenants where it has not been explicitly disabled.
La official one-time passcode documentation specifies that the code is valid for thirty minutes and that the session expires after twenty-four hours. This mechanism is an authentication method for a B2B guest; it does not turn an “Anyone” link into an identified link. Do not therefore confuse the sign-in experience with the scope of authorisation.
Test the invitation with a real external account, a personal address and a partner managed by another organisation. Also check conditional access rules: an overly strict requirement can block the partner, while an overly broad exception can weaken protection across all resources.
How do you combine MFA, conditional access and devices?
Conditional Access policies can require multi-factor authentication for guests and control sessions. For collaboration with a known Microsoft Entra organisation, cross-tenant settings can determine whether certain claims from the originating tenant are trusted. The choice depends on the risk, partner and resources involved.
Do not assume that an external device will be managed by your organisation. For sensitive data, examine session restrictions, web access, downloads and permitted applications. Test the experience on a managed workstation, personal device and private browser. A technically correct but incomprehensible rule generates workarounds via email or personal storage.
Apply the policy to the correct scope and test every change with pilot users.
How should you classify documents before sharing them?
The sharing decision should derive from sensitivity. Create understandable categories, such as public, internal, confidential and highly restricted, and associate each with permitted sharing methods. The name matters less than users being able to recognise a document and apply the rule without consulting a thirty-page manual.
Personal data remains subject to GDPR principles, including purpose limitation, data minimisation, accuracy, storage limitation and security. Sharing with a supplier does not remove the need to identify their role, the need, duration and measures. The official regulation remains the legal source; sensitive cases require the DPO or appropriate legal counsel.
Avoid relying solely on the filename. The library, site, owners and labels should all reflect the same policy. For a mixed batch, separate the shareable document from the folder containing internal notes, identity documents or working versions.
Who can share and who should review access?
The tenant defines who can invite external users; the site can further restrict who is authorised to share. An organisation can restrict new guest invitations to owners while allowing members to share with existing guests. The appropriate delegation depends on the number of sites, maturity level and available support.
Name at least two owners for each external site. The business owner validates the need and members; IT maintains the rules, reports and mechanisms. Plan for replacing an owner who leaves the organisation. Sites without an owner should be suspended, reassigned or archived according to a defined procedure.
Train users to choose the link, permission and duration, and then remove access.
How should expiry and review be organised?
Every external access should have an end event: project date, contractual deadline, delivery or periodic review. Technical expiry helps, but it does not know whether the business need continues. A review requires the owner to confirm, remove or extend access with a simple justification.
Segment reviews by site and owner. Start with anonymous links, sites open to new guests, inactive users and ownerless spaces. Do not delete blindly: some folders support an obligation or active relationship. Provide enough context to make a decision, then log the action.
Measure access removed, extended and unanswered. Sensitivity, scope and lack of ownership matter more than the number of links.
How do you test the configuration before general rollout?
Create a pilot site without real data and test the four sharing levels, different links, read, edit, expiry, message forwarding, revocation and owner changes. Use external accounts covering several identity types. Check what the recipient sees and what the administrator can retrieve.
Also test errors: invitation to the wrong address, partner blocked by a policy, prohibited domain, existing guest, expired link, moved file and absent owner. The expected result should be written before the test. A screenshot or log provides evidence of the behaviour instead of relying on memory.
The visual below shows a minimal decision path. GVISION recommends piloting one site and one business group, then expanding after validating the rules, help messages and removal procedures.

Which Belgian scenarios illustrate the choices?
A firm shares a collection folder with an identified client: “Specific people” and an end date. A school opens a project space to a service provider for one term: B2B guest in a dedicated group. An ASBL distributes an already-public report: a time-limited anonymous link may be acceptable if the organisation wants simple distribution.
A multi-site group exchanges plans with several contractors: separate external site, groups by work package and internal owners. A healthcare organisation sends a document containing personal data: identified recipients, minimum scope and validation of the processing framework. An administration publishes a blank template: a public channel rather than a collaboration link maintained indefinitely.
Partner status does not justify access to all resources.
What mistakes should be avoided?
Avoid using an “Anyone” link out of habit, granting edit access without a need, adding a guest directly to several resources, sites without owners, cascading permission exceptions and sharing without an end date. Do not consider an email address sufficient proof for every sensitive action.
Do not make the entire tenant permissive to resolve a problem on a single site. Do not confuse “people with existing access” with a new authorisation. Do not share a parent folder when only one file is required. Do not let an authentication error push users towards their personal email.
Finally, do not launch a review without the ability to make decisions. Give owners the site name, resource, recipient, link type, available last activity and consequence of removal.
Frequently asked questions
Does a guest need a Microsoft 365 licence?
Not necessarily to access shared content. However, the required licences and features depend on the services, policies and capabilities used.
Can a “Specific people” link be forwarded?
The message can be forwarded, but only authorised recipients should be able to open the content after verification.
Is an “Anyone” link always prohibited?
No, but it is unsuitable for content requiring identity, confidentiality or individual traceability. Use it for non-sensitive content and with a controlled duration.
What is the difference between a guest and a specific link?
A guest is a manageable identity object in Entra and can belong to groups. A specific link authorises named people on a particular resource.
Can MFA be enforced for guests?
Yes, Conditional Access policies can target guests. They should be tested with the partner identities actually used.
What happens when an owner leaves the company?
A second owner must be able to take over the review. Without a replacement, the site should be reassigned, suspended or archived according to the procedure.
How often should access be reviewed?
There is no universal frequency. Use the project deadline and content risk, with more frequent reviews for sensitive spaces.